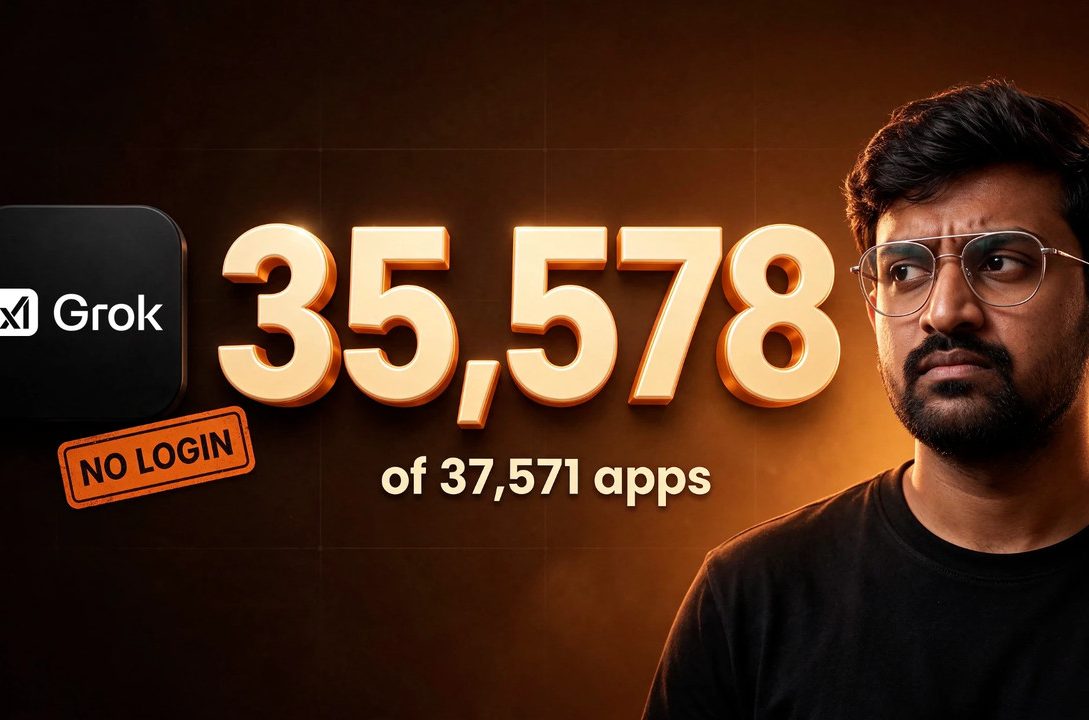
The Grok leak is real, but it isn’t a hack. Security firm Claroc says 35,578 of 37,571 live apps built with Grok opened for anyone with no sign-in, including 24 apps made by staff at SpaceXSI, the company behind Grok. Your normal Grok chats aren’t what spilled. This is news, not legal advice.
Key takeaways
- The Grok leak: on 10 November 2026, Claroc said 35,578 of 37,571 live Grok-built apps (94.7%) opened without any sign-in.
- What was inside: most apps were games, landing pages and calculators. About 1 in 10 held internal or personal data, and Claroc rates roughly 2% as high or critical.
- Why: Claroc says the publish screen had “Anyone with the link” preselected, and every app’s address sits in public DNS records.
- Response: SpaceXSI removed its own 24 staff apps. It says apps stay private until a creator shares them.
- Do now: if you published an app with Grok, set it to “Invited users” or “Only you” and test the link in a private window.
Last updated: Sunday 15 November 2026, IST. Status: findings published by Claroc and reported by Ars Technica and The Hacker News. Not independently verified by Askhari. No public change to Grok’s default confirmed yet.
Table of Contents
Table of Contents
What’s the Grok leak?
The Grok leak is the exposure of tens of thousands of apps that people built and published with Grok, the AI assistant from SpaceXSI (the company formerly called xAI). On 10 November 2026, Claroc said 35,578 of 37,571 live Grok-built apps opened for anyone, with no login. Claroc says it loaded each first page once, like any visitor would.
Grok can write a working app from a description typed into its chat. The Hacker News reports the company opened this chat-based builder to every Grok plan on 19 August 2026. Each published app gets its own address ending in grok.me.
Picture each app as a house with four random words painted on the door. You might expect a lock to help, and one exists. It just came open by default, and the street directory listed every house name.
Grok Build apps and the Grok Build coding tool are two different things
News headlines call the exposed apps “Grok Build apps”. The Cloud Security Alliance, in its research note on the exposure, points out that this chat-based builder shares a name with a separate terminal coding tool called Grok Build. That tool had its own problem in July 2026, covered in the timeline below.
This post is about the apps. If you only chat with Grok, or follow other xAI news such as the Grok Imagine Odyssey episode, this specific Grok leak didn’t expose your chats.
What did the Grok leak expose?
Most open apps were harmless games, landing pages and calculators, so the headline number looks scarier than the typical app. About 1 in 10 held internal business or personal data. Claroc estimates roughly 2% held material it rates high or critical, which it extrapolates to 650 to 800 apps.
| Measure | Number | Who says |
|---|---|---|
| grok.me names listed | 43,601 | Claroc |
| Apps still online when tested | 37,571 | Claroc |
| Apps open without sign-in | 35,578 (94.7%) | Claroc |
| Apps that answered with an access error (HTTP 401) | 1,993 (5.3%) | Claroc |
| Open apps with internal or personal data | About 1 in 10 | Claroc |
| Open apps rated high or critical | About 2% (650 to 800 estimated) | Claroc, extrapolated |
| Apps built by SpaceXSI and X staff | 24 | Claroc |
| Other organisations identified | 30 (26 with 1,000+ staff, 6 in the Fortune 500) | Claroc |
Claroc says it confirmed several examples by hand. It blurred personal details in its screenshots and published no app addresses.
- A hospital group’s event app with a searchable roster of more than 3,500 employees.
- An intensive care briefing for one patient, with labs, imaging and ventilator status.
- A fire department’s live shift board, listing firefighters by name and badge number.
- A trucking firm’s recruiting list of more than 1,000 people, with legal names and personal email addresses.
- A contractor’s timesheet app whose code held 18 accounts with plain-text passwords, administrators included.
Claroc says it didn’t sign in, submit forms or use any password it saw on third-party apps. It tested edits and deletes only on two apps it built itself, with made-up data.
Why were Grok apps open to anyone in the Grok leak?
Claroc points to two causes that stacked on each other. First, the access panel shown at publishing had “Anyone with the link” already selected. Second, every app’s address is a public DNS record, so strangers can list it without being given the link.
DNS is the internet’s phone book. You type a name, and it tells your computer where to go. Passive DNS services log lookups from the resolvers they run or buy, and anyone with an account can search those logs by pattern. Claroc says the first time the intended people opened a link, its name landed in a commercial index.
- A user describes an app to Grok and publishes it from the same chat window.
- Grok proposes four random words as the address, such as a made-up four-word name followed by grok.me.
- In the paid account Claroc used, the access setting was already “Anyone with the link”.
- The first visit makes a DNS lookup, and passive DNS services record the name.
- A researcher searches those records for names ending in grok.me and gets a list of live apps.
Ars Technica adds a design point. The random words sit to the left of the domain. Google Docs and the share links of Claude, ChatGPT and Gemini keep the secret to the right, in the path, so DNS never sees it. The Ars report puts four random words at roughly 38 bits of randomness, which is hard to guess but irrelevant once the names are listed.
Did the generated sign-in make apps safe?
Not in Claroc’s test, and that’s the surprising part. It asked Grok for a customer list “for my company’s sales team of 4 people”. Grok added “Continue with Google” and “Continue with X” buttons on its own. Claroc says the code added each person who signed in to the team before checking whether they belonged, so the check always passed.
A Google account that was never invited then read every record, edited one and deleted another. Claroc proved this only on its own test app.

Were SpaceXSI’s own apps part of the Grok leak?
Yes. Claroc found 24 open apps built by SpaceXSI and X staff, including a confidential onboarding plan for a new enterprise sales hire and a sales territory map of 594 accounts. SpaceXSI took all 24 down after the report. It had not, by Claroc’s account, done the same for other users’ apps.
- An onboarding plan marked confidential, with internal system addresses and 19 internal chat channels.
- Eight X advertising proposals and media plans, one addressed to a US federal agency and marked confidential.
- Four live advertiser boards with campaign spend, one tracking progress toward a $1.6 million sales goal.
- Seven campaign reports for advertisers in Brazil, Japan, Korea and Thailand.
- Two copies of an X brand safety playbook labelled as an internal sales hub.
Only one SpaceXSI or X app, an archive of ad measurement studies, asked for a password. Claroc says it reported two of the apps on 8 November and the other 22 on 9 November. Ars Technica reports that removal began within hours of its own email to the company, and that all 24 returned “app not found” by publication.
What does SpaceXSI say about the Grok leak?
SpaceXSI says Grok apps stay private until their creator shares them, and that employee accounts default to “Only you”. Claroc agrees nothing goes public before the creator clicks Publish. Its objection is to the next step, where “Anyone with the link” was already selected in the account it used.
According to Claroc, the company described publishing as several steps: click Publish, pick an address, click Publish again, choose between “Only you” and “Anyone with the link”, accept a legal disclaimer and publish a final time. A Cursor representative told Ars Technica that apps are “private by default and nothing goes public unless the creator chooses to share it”, and that ChatGPT, Lovable and Bolt also offer shareable links. The Next Web notes Cursor is the coding company SpaceX bought in August.
“…the default answer to who can see it’s everyone.”
Asaf Aprozper, Claroc co-founder and CTO, on AI app builders. Source: Claroc report, 10 November 2026.
Claroc’s reply is that the people who published the 35,578 open apps went through every one of those steps. Ars Technica reports that Claroc’s CTO tested the flow and found users had to change “Anyone with the link” themselves. Claroc also agrees the exposure isn’t unique to Grok, but says “Grok is where we found by far the most sensitive company data.”
One more fact belongs here. Claroc sells tools that secure AI-built apps, and its report ends with an offer of a paid exposure check. Its findings still come with method notes and a named researcher. So treat the numbers as a vendor’s research, the way the Cloud Security Alliance does, and don’t quote them as settled fact.
Claroc asked SpaceXSI for four changes: serve shared apps on a hard-to-guess path under one host, add an “everyone in my organisation” option, make “Only you” the default, and warn when an app has a database but no sign-in. We found no public confirmation by 15 November that any of the four fixes to the Grok leak has shipped.
Grok leak timeline: what happened and when?
The Grok leak was found on 8 November 2026 and published two days later. It sits inside a longer run of Grok exposures that start in 2025. The table keeps the dates and sources in one place.
| Date | What happened | Source |
|---|---|---|
| 14 Jul 2026 | Researcher reports the Grok Build coding tool, version 0.2.93, uploaded whole Git repositories. One test sent 5.10 GiB while model traffic was about 192 KB. A server setting turned uploads off on 13 July. | The Hacker News |
| 19 Aug 2026 | Grok’s chat-based app builder opens to all Grok plans. | The Hacker News |
| 18 to 22 Oct 2026 | Claroc shows Meta Muse share pages can be found through passive DNS. Meta disables sharing, then reissues shared items at new addresses. | The Hacker News |
| 8 Nov 2026 | Claroc finds the Grok leak and reports it, including two SpaceXSI apps. | Claroc |
| 9 Nov 2026 | Claroc reports the other 22 staff apps. | Claroc |
| 10 Nov 2026 | Claroc publishes. Ars Technica reports. SpaceXSI starts removing its 24 apps within hours of Ars’s email. | Claroc, Ars Technica |
| 11 Nov 2026 | The Hacker News, Engadget, TechRadar and the Cloud Security Alliance cover it. | Multiple outlets |
| 15 Nov 2026 | Askhari finds no public confirmation of a new default or of owner notifications. | Askhari check |
Is the Grok leak a hack or a data breach?
Claroc describes the Grok leak as an exposure, not a hack. The Cloud Security Alliance says no attacker had to bypass any control, because the data sat in apps that opened for any visitor. Whether it counts as a legal “data breach” depends on the law, the data and what happened next.
| Myth | What the sources say |
|---|---|
| Grok was hacked. | Claroc and the Cloud Security Alliance describe a design and default problem. Apps opened like any web page. |
| My Grok chats leaked. | The Grok leak concerns apps built with the app builder. It isn’t about ordinary Grok conversations. |
| All 35,578 apps held private data. | Most were games, landing pages and calculators. About 1 in 10 held internal or personal data. |
| Criminals stole the data. | No public evidence either way. CyberInsider notes the findings show data was reachable, not that anyone copied it. |
| SpaceXSI took everything down. | Per Claroc, only the 24 staff apps were removed. Other users’ apps stayed open at publication. |
How does this Grok leak compare with earlier Grok exposures?
This is at least the fourth widely reported Grok exposure since 2025, and each had a different cause. Counting the Grok leak of November 2026, the pattern is a convenience feature shipped with a loose default.
| When | Exposure | Cause as reported | Source |
|---|---|---|---|
| Jul 2025 | An xAI API key reached public GitHub, giving access to at least 52 models | A US government employee published the key | Obsidian Security, OECD.AI |
| Aug 2025 | Shared Grok chats appeared in Google search | Share links were indexable. Forbes and Fortune say 370,000+, the BBC says nearly 300,000 | BBC, Forbes, Fortune |
| Jul 2026 | Grok Build coding tool uploaded whole Git repositories | Default upload behaviour in version 0.2.93, switched off server-side | The Hacker News |
| Nov 2026 | Grok-built apps open to anyone | Default access setting plus public DNS names | Claroc, Ars Technica |
The 2025 and 2026 chat and repository incidents are separate from the Grok leak of November 2026. They show how earlier defaults were handled. In July, xAI turned uploads off with a server setting, and The Hacker News reported it had not said why full repositories were uploaded by default.

Do ChatGPT, Gemini and Claude share links have the same problem as the Grok leak?
Per Claroc, shared chats on ChatGPT, Gemini and Claude keep the secret part of the link in the path, so DNS never sees it. Published apps are different. Grok, ChatGPT, Lovable, Replit, Base44, Google AI Studio and Meta’s Muse give each app its own hostname, and v0 and Bolt deploy to hostnames too.
If you use ChatGPT’s private features, our guide to ChatGPT locked chats explains what a PIN protects and what it doesn’t. Meta’s Muse family is covered in our Meta Muse Wonder explainer, though that post is about the model, not the link-sharing fix.
| Product | Where the secret sits | Default when Claroc tested |
|---|---|---|
| Grok apps | Left of the domain: name.grok.me | “Anyone with the link” preselected in a paid account |
| ChatGPT apps | Two-level hostname: app.username.chatgpt.site | “Only me” until changed |
| Claude published artifacts | In the path: claude.ai/public/artifacts/id | Not an app hostname |
| ChatGPT shared chats | In the path: chatgpt.com/share/id | Not an app hostname |
| Gemini shared chats | In the path: gemini.google.com/share/id | Not an app hostname |
So the lesson of the Grok leak is narrower than “AI links are unsafe”. A discoverable address only becomes a data exposure when the access control behind it’s open. Claroc says ChatGPT’s default of “Only me” is what kept a found address from leading to data.
How can you check whether your Grok app is open after the Grok leak?
Open each app you published and read its access setting. If it says “Anyone with the link”, treat the app as public. These steps, drawn from the Grok leak research, follow Claroc’s own checklist, and Claroc is a security vendor, so test them on your own apps only.
- List your apps. Open every app you published with Grok and read the access setting. “Anyone with the link” means open to everyone who finds the address.
- Test as a stranger. Open the app in a private or incognito window where you’re signed in to nothing. If it loads, anyone can see it.
- Lock it. Switch to “Invited users” or “Only you”. In Claroc’s tests, “Only you” made a stranger get an error, and unpublishing took an app offline within seconds.
- Test sign-in from outside. Try a Google account that isn’t on your team list. If it gets in, the app checks who you’re but not whether you belong.
- Search the scripts. Look in the app’s files for names, emails and passwords. Change any password you find, because it was readable while the app was public.
- Delete what shouldn’t be there. Remove patient, customer, staff or ID data from any app that has no real company sign-in.
Menu names change, so look for the labels Claroc names rather than a fixed path. If you can’t find the setting, unpublish the app until you can.
What are the most common link mistakes behind the Grok leak?
- Treating a random-looking address as a password. It’s a name, and names can be listed.
- Assuming a sign-in button means access control. Claroc’s test showed a login that didn’t check membership.
- Pasting real customer, staff or patient lists into a quick AI-built tool.
- Forgetting that apps change with each prompt. An app that was harmless yesterday can hold customer data today.
- Leaving old test apps published after the demo is over.

What does the Grok leak mean for India?
Claroc doesn’t say any Indian organisation was hit by the Grok leak. It says 12 of the 30 organisations it identified are outside the US, in 11 countries, and it names none. Indian teams that build apps with AI face the same default risk, and India’s DPDP Rules add breach duties from May 2027.
India has two relevant rules. The CERT-In direction of 28 April 2022 already asks named organisations to report listed incidents within six hours. The Digital Personal Data Protection Act, notified on 13 November 2025, starts its security-safeguard, breach-notice and penalty provisions 18 months later, in May 2027.
| Rule | What it asks | Status |
|---|---|---|
| CERT-In direction, 28 Apr 2022 | Report listed incidents within six hours | In force |
| DPDP Act, section 8(5) | Take reasonable security safeguards. Penalty up to ₹250 crore | Starts May 2027 |
| DPDP Act, section 8(6) | Tell the Data Protection Board and each affected person of a breach. Penalty up to ₹200 crore | Starts May 2027 |
Practical rule after the Grok leak for a freelancer, student founder or small business in India: don’t put client data, staff lists, health records or ID numbers into an AI-built app unless it has real sign-in and a membership list. A vibe-coded tool is still a system holding personal data.
Who is affected by the Grok leak, and who isn’t?
| Person or team | Affected by this exposure? | Why |
|---|---|---|
| You only chat with Grok | No, not by the Grok leak | The findings concern apps published with the builder |
| You published a Grok app with “Anyone with the link” | Possibly | Open apps could be opened without sign-in |
| Your staff built apps on Grok without IT knowing | Possibly | Claroc says builders need no admin rollout or company account |
| You’re named in someone else’s open app | Possibly | Rosters, lists and records sat inside open apps |
| You use ChatGPT, Gemini or Claude share links | Not by this mechanism | Claroc says their share secrets sit in the path, not the hostname |
Watch: how Claroc found the Grok leak

What happens next after the Grok leak?
If you build with AI tools, you’ll want to watch these. They’re items to watch, not predictions. As AI agents take actions for people, as seen when United banned AI agents from booking flights, defaults in shared and published tools matter more.
- Whether SpaceXSI makes “Only you” the default for everyone, as Claroc asked.
- Whether SpaceXSI tells the owners of the other open apps, which Claroc says it didn’t commit to.
- Whether other builders such as Lovable, Replit or Bolt change defaults or address layouts.
- Whether any regulator or affected organisation comments publicly.
Askhari will update this Grok leak explainer on the same URL with dated notes if the default changes or new facts appear.
Related reading on Askhari
- Grok Imagine Odyssey: what the 7-minute xAI episode really shows, the latest xAI product story before the Grok leak.
- ChatGPT locked chats: how the PIN works and what it doesn’t protect, on privacy features in a rival chatbot.
- Meta Muse Wonder: price, benchmarks and who can use it, on the model whose share links Claroc researched in October.
- PHP2Shell: why two critical PHP flaws need immediate attention, another security story where patching and defaults matter.
- United AI agent ban: what you can still do, on what happens when AI agents act on your behalf.
What we don’t know yet
- Whether anyone copied data from the open apps in the Grok leak. No public evidence either way.
- Whether SpaceXSI will change the default setting or notify owners of the other open apps.
- How many of the roughly 650 to 800 high or critical apps are real. Claroc used an AI classifier checked against a hand-read sample and then extrapolated.
- Whether any Indian organisation was affected. Claroc names no victims.
- Whether the Grok leak figures hold up under independent checks. The Cloud Security Alliance says it hasn’t verified them.
Grok leak FAQ
Was Grok hacked?
No hack has been reported in the Grok leak. Claroc and the Cloud Security Alliance describe apps that opened for any visitor, with no control bypassed. The problem is a default setting and public DNS names, not a break-in.
Did the Grok leak expose my Grok chats?
Not according to the reporting. The Grok leak concerns apps built and published with Grok’s app builder. A separate 2025 incident saw shared Grok chats appear in search results, so avoid sharing chats that hold private details.
Is Grok safe to use?
If you only chat, the Grok leak isn’t something you need to act on. If you publish apps with real company or personal data, you should set “Only you” or “Invited users” and test it from outside. The earlier Grok exposures show why checking defaults is sensible with any new tool.
Which other AI app builders have the same issue as the Grok leak?
Claroc says Lovable, Replit and Bolt also give each app its own address, so the same DNS records expose them. It says Grok is where it found by far the most sensitive company data, and that ChatGPT apps defaulted to “Only me”.
Can I see if my company was one of the 30 in the Grok leak?
No public list exists. Claroc withheld all app addresses and titles and says it emails affected organisations itself. Check your own staff’s apps instead, using the steps above.
Hari’s take
The takeaway from the Grok leak isn’t that one chatbot is bad. It’s that a default decides what most people do. When a publish screen preselects “Anyone with the link”, most people will keep it. SpaceXSI says it uses “Only you” for staff, yet 24 staff apps were still open, which tells me the default alone didn’t save even the builders.
I haven’t tested Grok’s screen myself, so I’m relying on Claroc’s tests and on the outlets that read them. If you’ve ever kept a preselected option on a busy day, you’re not alone. Before you share any AI link or app this week, open it in a private window and see what a stranger sees. Have you ever shared an AI chat or app link? Tell me yes or no in the comments, and name the tool.
Sources: Claroc, GhostShares 2, 10 Nov 2026 · Ars Technica, 10 Nov 2026 · The Hacker News, 11 Nov 2026 · Cloud Security Alliance, 11 Nov 2026 · CyberInsider, 12 Nov 2026 · The Next Web, 12 Nov 2026 · The Hacker News, 14 Jul 2026 · Obsidian Security · BBC, 21 Aug 2025 · Cybersecurity ASEAN, DPDP guide. Last updated 15 November 2026.